Marketplace compliance means meeting the privacy, platform and payment rules that apply to the people who use your site. For most classifieds sites and small marketplaces, compliance for platforms and marketplaces comes down to a few core things: handle personal data the way the GDPR and US state privacy laws expect, deal with reports of illegal listings under the EU Digital Services Act (and the UK Online Safety Act if you have UK users), know when trader rules such as the US INFORM Consumers Act apply, keep card payments with a regulated provider that handles strong customer authentication, and protect accounts with basic security such as two-factor authentication. This guide explains each rule as it stands in October 2026 and what it asks of a marketplace owner. It is part of our guide to building trust in a marketplace.
This is general information, not legal advice. Which rules apply depends on where you and your users are, your size and how your site works. Check with a lawyer before relying on any of it.
In short
- The GDPR covers any site with EU users whatever its size: get consent before ad trackers, offer data download and deletion, and report breaches within 72 hours.
- Under the EU Digital Services Act every platform needs a Report button on listings and must tell sellers why a listing was removed, while trader rules spare micro and small enterprises.
- The CCPA applies only above 26,625,000 dollars revenue or data on 100,000 or more Californians, and the US INFORM Act mainly affects sites that process seller payments.
- Never handle card numbers yourself: use a regulated provider with strong customer authentication so you can validate PCI DSS with the short SAQ A questionnaire.
- Turn on two-step login for every admin and moderator first, prefer authenticator apps or passkeys over SMS, and revoke access the day someone leaves.
Part of the guide Trust and safety for your marketplace · Part 4 of 8 Next: How to Handle Disputes in a Marketplace: A Practical Guide →
Which laws apply to your marketplace?
A marketplace usually falls under the law of the place where its users are, not only where the owner is based. A site run from Spain with buyers in California, or a US site with sellers in Germany, can be covered by rules from both places. The table gives an overview; each law is explained below.
| Rule | Who it covers | Main duties for a marketplace | Status (October 2026) |
|---|---|---|---|
| GDPR (EU) | Any site handling personal data of people in the EU, whatever its size | Lawful basis and consent, data minimisation, user rights, security, 72-hour breach notice | In force since 25 May 2018 |
| CCPA/CPRA (California) and other US state laws | Businesses above revenue or data-volume thresholds | Notice, access and deletion rights, "Do Not Sell or Share" opt-out, honouring Global Privacy Control | New CCPA regulations in force since 1 January 2026 |
| COPPA (US) | Sites aimed at, or knowingly collecting data from, children under 13 | Verifiable parental consent, written data retention policy | Amended rule: compliance required since 22 April 2026 |
| EU Digital Services Act | Every hosting service and online platform with EU users | Notice-and-action, statements of reasons; trader traceability for larger marketplaces | Applies to all platforms since 17 February 2024 |
| UK Online Safety Act | User-to-user services with links to the UK | Illegal content risk assessment and safety duties; child safety duties if children are likely to use the site | Illegal content duties since 17 March 2025; child safety duties since 25 July 2025 |
| INFORM Consumers Act (US) | Marketplaces with "high-volume" third-party sellers | Collect and verify seller bank, tax and contact details; disclose larger sellers | In force since 27 June 2023 |
| PSD2 strong customer authentication (EU/UK) | Payment providers, and so every card checkout in Europe | Use a provider that supports 3-D Secure and other SCA methods | Enforced for e-commerce since 1 January 2021 (EU) and 14 March 2022 (UK) |
| PCI DSS v4.0.1 | Anyone accepting card payments | Keep card data off your servers; validate with your provider | All v4 requirements mandatory since 31 March 2025 |
GDPR for marketplaces
The General Data Protection Regulation applies to any business that offers goods or services to people in the EU or monitors their behaviour, wherever the business is located. Unlike most US laws, it has no revenue threshold: a small classifieds site with EU users is covered.
Collect less, and say why you collect it
Every piece of personal data needs a lawful basis, such as running the user's account (contract), a legal obligation or consent. Collect only what each category really needs: a contact method and a location are usually enough for a classified ad. If you verify sellers to reduce fraud, ask only for the documents you need and delete them once you have decided. Publish a plain-language privacy policy that lists what you collect, why, how long you keep it, and every third party you send it to, including analytics, email and payment providers.
Ask before loading ad and analytics trackers
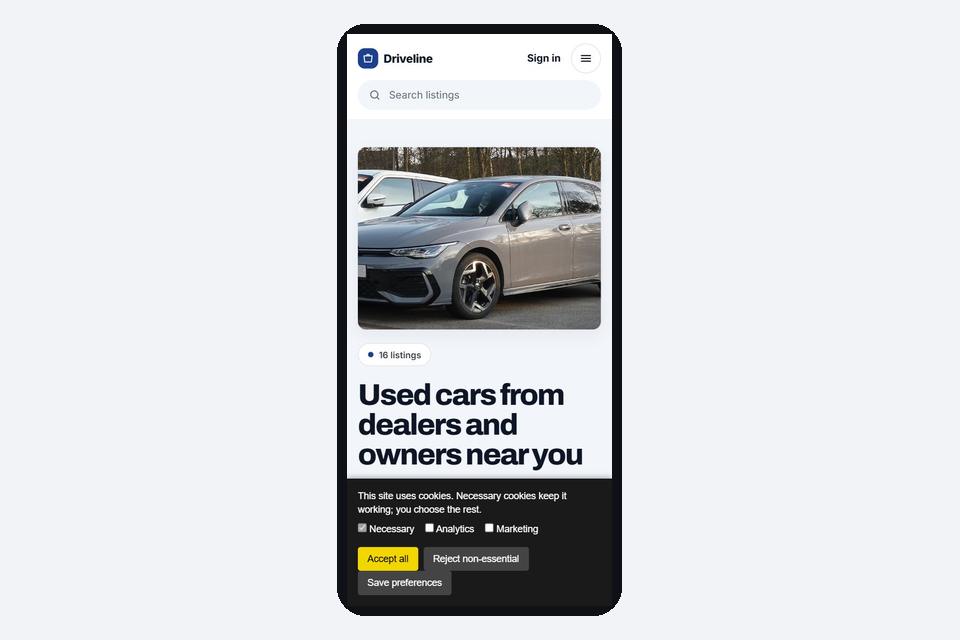
Personalised ads and third-party trackers need prior consent from EU visitors, given through a cookie banner that makes refusing as easy as accepting. The largest marketplace case shows why. In July 2021 Luxembourg's data protection authority (CNPD) fined Amazon EUR 746 million for using personal data for behavioural advertising without a valid legal basis. On 12 March 2026 Luxembourg's administrative appeal court annulled the fine because the regulator had not first analysed whether the violations were intentional or negligent. The court still confirmed most of the underlying violations and sent the case back to the regulator, which can issue a new decision (PPC Land, March 2026; Paperjam). The lesson for a small marketplace: get consent first; "legitimate interest" did not hold up for ad tracking even for Amazon.
Give users control over their data
The GDPR gives users the right to access their data, correct it, have it deleted, and receive a copy in a machine-readable format. The easiest way to meet these rights is in the account settings: a "download my data" button, an edit profile page and an account deletion option. A self-service process is faster for users and leaves fewer requests for you to answer by hand. Most marketplaces also need a written record of their processing activities, since the exemption for organisations under 250 staff does not cover regular processing.
Plan for a breach before it happens
If personal data is lost or exposed, you must tell your data protection authority within 72 hours of becoming aware of it, unless the breach is unlikely to put anyone at risk, and tell affected users without undue delay when the risk is high. Write down who decides, which authority you would notify and how you would contact users. Breaches are common: DLA Piper's January 2026 survey counted an average of 443 breach notifications a day in Europe, up 22%, and about EUR 1.2 billion in GDPR fines in 2025 (EUR 7.1 billion since May 2018). The maximum fine is EUR 20 million or 4% of worldwide annual turnover, whichever is higher.
CCPA, CPRA and US state privacy laws
The California Consumer Privacy Act, as amended by the CPRA, covers a for-profit business that does business in California and meets one of three tests: annual gross revenue over $26,625,000 (the 2025 adjusted figure), buying, selling or sharing the personal information of 100,000 or more California consumers or households, or earning half or more of its revenue from selling or sharing personal information. Most small classifieds sites fall below all three, but a site that sends visitor data to ad networks can reach the 100,000 test sooner than expected.
For covered businesses, the main duties are:
- Notice and rights. Tell users what you collect, and let them access, correct and delete it.
- "Do Not Sell or Share My Personal Information". The opt-out link must use this wording, and it covers sharing data for cross-context ad targeting as well as selling it. You must also treat a browser's Global Privacy Control signal as a valid opt-out (California Attorney General, page updated August 2026).
- Penalties. Fines are up to $2,663 per violation, or $7,988 for intentional violations and those involving consumers under 16 (CPPA, December 2024).
- New regulations since 1 January 2026. Risk assessments are required for risky processing from that date, with the first submissions due by 1 April 2028. Rules on automated decision-making technology apply from 1 January 2027. Cybersecurity audit certifications are due by 1 April 2028, 2029 or 2030, depending on revenue (CPPA, 23 September 2025).
California is no longer alone. About 20 states now have comprehensive privacy laws; IAPP counted 19 in January 2026, when the laws of Indiana, Kentucky and Rhode Island took effect (IAPP, January 2026). Thresholds differ: Indiana and Kentucky apply from 100,000 consumers in the state, Rhode Island from 35,000. Check the states where most of your users live.
If children under 13 could use your site, the amended COPPA Rule has applied in full since 22 April 2026. It requires separate verifiable parental consent before disclosing children's data to third parties, for example for targeted advertising, and a written data retention policy. Most classifieds sites avoid this by setting a minimum age in their terms and not targeting children.
In Canada, PIPEDA still governs private-sector privacy. Bill C-36, the Protecting Privacy and Consumer Data Act, was introduced on 15 June 2026 to replace PIPEDA's privacy rules, with penalties of up to the greater of CAD 10 million or 3% of global revenue for some breaches, but it is not law yet (Osler).
The EU Digital Services Act: rules for every marketplace
The Digital Services Act (DSA) has applied to all online platforms since 17 February 2024. Some duties apply to every site that hosts user content, including the smallest classifieds site:
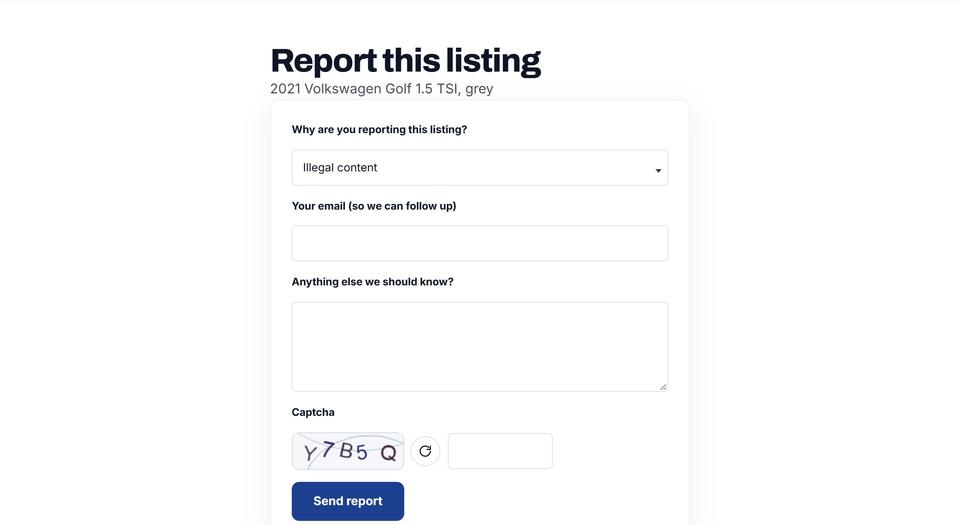
- Notice and action (Article 16). Give users an easy electronic way to report illegal content, such as a Report button on every listing, and act on reports promptly.
- Statement of reasons (Article 17). When you remove a listing, hide it or suspend an account, tell the user what you did, why, and how they can challenge it.
- Criminal offences (Article 18). If you learn of a threat to someone's life or safety, inform the police.
- Clear terms (Article 14) and a contact point (Articles 11 and 12). Explain your content rules and moderation in your terms, and publish an email address for users and authorities.
Larger platforms have more duties. Marketplaces that let consumers buy from traders must collect each trader's name, address, phone, email, ID document, payment account, any trade register number and a self-certification, make reasonable efforts to check them, and show buyers the trader's details (Article 30). These trader rules, and the extra duties for online platforms in Articles 20 to 28 such as internal complaint handling, do not apply to platforms that are themselves micro or small enterprises (fewer than 50 staff and no more than EUR 10 million turnover), unless they are designated as very large platforms (Articles 19 and 29). Even so, separating business sellers from private ones and showing business details is good practice, and buyers expect it. Our guide to moderation and marketplace policies covers how to set up reporting and review.
Template
Moderation and content-removal policy
Publish this so users know how listings are checked, how to report one and how to appeal a decision; fill in your timings and contact points.
A starting point, not legal advice: have it checked for your country.
The UK Online Safety Act
If your classifieds site lets users post listings or message each other and has a significant number of UK users (or targets the UK), it is a "user-to-user service" under the Online Safety Act 2023. According to Ofcom:
- Services had to complete an illegal content risk assessment by 16 March 2025, and the illegal content safety duties have applied since 17 March 2025. For a marketplace, the main risks are fraud, the sale of illegal items such as weapons or drugs, and harmful messages.
- Services had to carry out a children's access assessment by 16 April 2025. If children are likely to use the site, the child safety duties have applied since 25 July 2025.
- Ofcom can fine up to GBP 18 million or 10% of qualifying worldwide revenue, whichever is greater.
For a small site, the practical steps are a written risk assessment, a working reporting and takedown process, clear terms, and a minimum age if your site is not meant for children.
The US INFORM Consumers Act
Since 27 June 2023, US online marketplaces must collect a bank account, tax ID and contact details from each "high-volume" third-party seller within 10 days and verify them within 10 days of receiving them. A high-volume seller has 200 or more sales of new or unused consumer products and at least $5,000 in gross revenue in any continuous 12-month period in the last 24 months. Only sales processed through the marketplace count, so a classifieds site where buyers pay sellers directly may have few or no such sellers. Sellers must recertify their details every year, and sellers with $20,000 or more in annual revenue on the platform must have their name, address and contact details shown to buyers. The FTC can seek civil penalties of up to $53,088 per violation; the FTC kept its 2025 penalty amounts for 2026 (FTC business guidance).
Secure payments: PSD2, strong customer authentication and PCI DSS
The safest rule for a small marketplace is simple: never handle card numbers yourself. Let a regulated payment provider take card entry on its own hosted page or embedded form.
- Strong customer authentication (SCA). Under the EU's second Payment Services Directive (PSD2), most online card payments in Europe must be confirmed with two of three factors (something the buyer knows, has or is), usually through 3-D Secure in the bank's app. Enforcement for e-commerce began on 1 January 2021 in the EU and on 14 March 2022 in the UK. The duty sits with banks and payment providers, so in practice you need a provider that supports SCA. The EU agreed a revised framework (PSD3 and a Payment Services Regulation) in November 2025, which adds more fraud rules such as payee name checks, but as of October 2026 it does not yet apply.
- PCI DSS v4.0.1. All the future-dated requirements became mandatory on 31 March 2025. Merchants that hand all card entry to a provider can use the short SAQ A questionnaire. Since 31 March 2025 it no longer includes the payment-page script requirements (6.4.3 and 11.6.1); instead, merchants must confirm that their site is not susceptible to script attacks that could affect their e-commerce system (PCI Security Standards Council, January 2025).
Payment method matters for fraud too. The FTC received 3 million fraud reports in 2025, with $15.9 billion lost, and bank payments and cryptocurrency produced the highest losses (FTC, March 2026). The FBI's 2025 Internet Crime Report counted 56,478 complaints about non-payment and non-delivery, the fraud type closest to classifieds, with $503 million lost (FBI IC3). Card payments through a provider give buyers a way to dispute a charge; wire transfers, gift cards and crypto sent to a stranger usually do not. Warn users never to pay that way, and see our guide to preventing marketplace fraud and scams.
Template
Stay-safe tips page for buyers and sellers
Publish this as your safety page and link it from every listing and message screen; add your own payment and reporting details.
Marketplace data security basics
Privacy laws require "appropriate" security, and a breach is the fastest way to end up in front of a regulator. These are the basics that matter most for a marketplace.
Two-factor authentication
Two-factor authentication (2FA) asks for a second proof of identity after the password: something you have, such as a phone or security key, or something you are, such as a fingerprint. If a password is stolen or reused from another site, the attacker still cannot log in. On a marketplace this stops account takeovers, where scammers use a trusted seller's account to post fake listings or message buyers.
The US standard for digital identity, NIST SP 800-63B-4 (final version July 2025), no longer treats all second factors as equal:
| Method | Protection | Notes |
|---|---|---|
| SMS or voice codes | Basic | Classed as "restricted" because of SIM swaps and interception. Better than nothing; best kept as a fallback. |
| Authenticator app (one-time codes) | Good | Free and works offline. Codes can still be typed into a fake login page. |
| Passkeys and hardware security keys | Strongest | Phishing-resistant. NIST requires services at its AAL2 level to offer at least one phishing-resistant option. |
Passkeys are now common: in a 2024 survey for the FIDO Alliance, 53% of people said they had turned them on for at least one account. A practical rollout for a marketplace:
- Require two-step login for every admin and moderator account first. These accounts can export user data and change settings.
- Offer it to sellers next, starting with your most active ones, and explain the benefit when they sign up.
- Make an authenticator app the standard method, keep SMS as a fallback, and add passkeys when your platform supports them.
- Give users a recovery route (backup codes or a verified email) so a lost phone does not lock them out, and send an email alert whenever a factor is added or removed.
Passwords
NIST SP 800-63B-4 reverses two old habits. Services must not force password changes on a schedule (only when there is evidence of compromise) and must not impose composition rules such as "one uppercase letter and one symbol". Instead: at least 15 characters when the password is the only factor, or 8 when it is used with 2FA; allow long passwords, password managers and paste; check new passwords against a list of common and breached passwords; and limit failed attempts. Store passwords only as salted hashes, for example with bcrypt.
Encryption, access and offboarding
- Serve every page over HTTPS (TLS), including logins and messages.
- Give each team member their own account with only the access they need, rather than sharing one admin login.
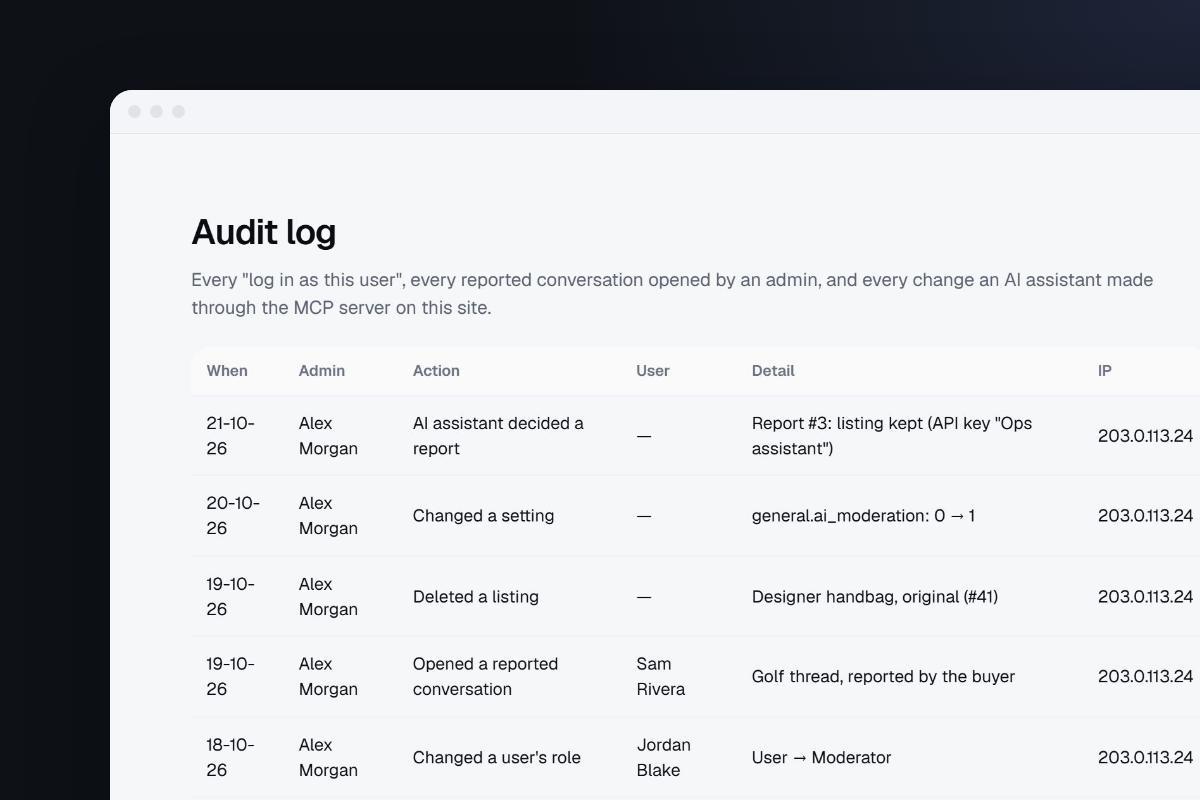
- Keep a log of admin actions so you can see who changed what.
- Revoke accounts, API keys and passwords the same day a staff member or contractor leaves.
Patching and backups
Keep your platform, plugins and server software up to date, or use hosting that does it for you. Keep a recent backup that the web server itself cannot overwrite, so ransomware cannot destroy it too.
Lessons from marketplace security breaches
Two well-documented marketplace breaches show where the risks are:
- eBay, 2014. Attackers used a small number of employee login credentials to reach a database holding names, encrypted passwords, email and postal addresses, phone numbers and dates of birth. eBay asked all of its users, reported as 145 million, to change their passwords, and several US state attorneys general opened inquiries (CNBC, May 2014). Lesson: staff accounts need 2FA as much as customer accounts.
- Coupang, 2025. At South Korea's largest online marketplace, a former employee kept access after leaving and used stolen security keys to reach customer data from June 2025. The breach was found in November 2025, and data linked to about 33.7 million accounts was exposed (names, contact details, delivery addresses and some order details, but not payment details according to the company). The CEO resigned in December 2025 and police raided the company's offices (BleepingComputer; Infosecurity Magazine). Lesson: offboarding and key management belong in your security plan.
The latest industry reports point the same way:
| Finding | Source | What it means for you |
|---|---|---|
| Exploited software vulnerabilities were the way in for 31% of breaches, overtaking stolen credentials for the first time | Verizon DBIR 2026 (incidents from November 2024 to October 2025) | Patching is now as urgent as 2FA |
| Ransomware was involved in 48% of breaches | Verizon DBIR 2026 | Keep backups the web server cannot overwrite |
| The average breach cost a record $4.99 million, up 12% | IBM Cost of a Data Breach 2026 | Prevention costs far less than a breach |
Two more lessons apply to every size of site: data you never store cannot leak, so collect less and let a payment provider hold card data; and when a breach happens, tell users quickly and plainly what happened and what they should do.
Terms, consumer law, tax reporting and data use
This page also replaces our older posts on the legal essentials for launching a classifieds marketplace, on cross-border rules for e-commerce and marketplaces, and on using and selling marketplace data ethically. The rules below come from those posts and add to the ones above. For cross-border payment fees, duties and shipping costs, see our separate guide to international payments.
Liability for listings and your terms of service
Marketplaces often fall under intermediary liability rules, so they are not directly responsible for what users post, but the protection varies by country. In the US, Section 230 of the Communications Decency Act gives online platforms robust protection. In the EU, the Digital Services Act sets out the duties for moderation and illegal content described above. The first DSA fine, EUR 120 million against X, was issued on 5 December 2025 (eucrim).
Your terms of service should also cover:
- Counterfeits and trademarks. Users may list fake or unauthorized products, or use brand names without permission. Give rights holders a clear way to report violations; in the US this is how you comply with the Digital Millennium Copyright Act (DMCA).
- Discrimination. Prohibit discriminatory language and behavior. Airbnb faced a backlash when hosts turned away renters based on race, gender or nationality, and responded with anti-discrimination policies and bias training for hosts.
- Paid listings and subscriptions. Charging for listings brings more responsibility for the accuracy and legality of what is posted. Subscription terms must be transparent to meet consumer protection laws such as the EU's Unfair Commercial Practices Directive.
Consumer protection when you sell across borders
Even if your company is based in one country, a global clientele can make you subject to rules in several. Many countries require clear return policies and disclaimers, such as the EU's 14-day "cooling-off" period, and the EU Consumer Rights Directive sets strict rules on returns, refunds and disclosures. In the US, the FTC enforces consumer protection and anti-fraud rules; in Canada, the Anti-Spam Legislation (CASL) regulates electronic marketing messages.
Two newer rules affect what listings must show:
| Rule | In force | What it means for a marketplace |
|---|---|---|
| EU General Product Safety Regulation | 13 December 2024 | Marketplaces need a single contact point for authorities, must show manufacturer and EU operator details on listings, and must inform buyers directly about recalls (Linklaters). |
| China: amended Cybersecurity Law | 1 January 2026 | Maximum fines for general security breaches by non-critical operators rise from RMB 100,000 (about USD 14,100) to RMB 2 million (about USD 282,000), and the law now covers any overseas activity that harms China's cybersecurity (DLA Piper). |
Tax registration and seller reporting
Depending on the country, you may have to collect sales tax, VAT or GST at the point of sale, and in the US each state sets its own threshold for sales tax registration. Platforms may also need to collect and remit taxes for users, depending on whether they act as a facilitator or an intermediary. Two reporting rules apply to platforms that handle seller payments:
| Rule | In force | What it means |
|---|---|---|
| EU DAC7 seller reporting | 1 Jan 2023 | Platforms that handle or can determine the payment report seller data to tax authorities by 31 January each year. Sellers of goods with fewer than 30 sales and no more than EUR 2,000 are excluded; services and rentals have no threshold (AVASK). |
| US Form 1099-K | Law signed 4 Jul 2025 | The reporting threshold is back to $20,000 and 200 transactions, replacing the planned $600 (Avalara, July 2025). |
Know whether you touch the money. INFORM, DAC7 and 1099-K mainly bite when your platform processes payments for sellers. A listings-only site that lets buyers and sellers pay each other directly carries far lighter tax-reporting duties than one with checkout or escrow. If you do host professional sellers, collect their trader details (company name, registration number, address) at signup: adding them once you have thousands of sellers is much harder.
Using and selling marketplace data
Ads and data deals bring extra rules on top of consent:
- Ads under the DSA. The European Commission states that the DSA bans targeted ads to children and ads based on sensitive data such as sexual orientation, religion or race, and requires ads to be labelled, showing who placed them and why the user sees them (European Commission, DSA policy page). Micro and small enterprises are exempt from most of the extra platform duties (Regulation (EU) 2022/2065, Article 19), but the exemption ends as you grow. If you cannot tell whether a user is a minor, default to contextual ads based on the category or search, not the person.
- Selling data in California. Under the Delete Act, businesses that qualify as data brokers register each January and pay a $6,000 annual registration fee (plus a processing fee). From August 1, 2026 they must access the state's Delete Request and Opt-out Platform (DROP) at least once every 45 days and process consumers' deletion requests (CPPA data broker page). Selling user data to third parties can put you in this category, so keep any insights you sell truly aggregated.
- Automated decisions. Under the new CCPA rules, personalization and scoring models need documentation, not just a line in the privacy policy (California Privacy Protection Agency). Write down what data goes into ranking sellers or flagging users, what it decides, and how a user can object.
- AI chatbots. Under the EU AI Act, bans have applied since 2 February 2025 and transparency rules since 2 August 2026: if you run an AI chatbot, users must be told they are talking to a machine (European Commission).
Sponsored listings are the lowest-risk way to earn from data, because they use the seller's money, not the buyer's personal data; label them clearly as ads. For most small and niche marketplaces, the practical order is to earn from listings, featured placements and memberships first, and treat third-party data sales as a later option that needs a legal review.
A marketplace compliance checklist
For a small classifieds site or marketplace, this order covers the most ground (not legal advice):
- Turn on two-step login for every admin and moderator account.
- Keep card payments on a regulated provider's hosted checkout that supports strong customer authentication.
- Show a cookie banner that asks before loading ad or analytics trackers, and honour Global Privacy Control.
- Collect only the fields your categories need, and delete verification documents once checked.
- Publish a plain-language privacy policy and terms that explain your content rules and moderation.
- Offer "download my data" and account deletion in the user's account.
- Add a Report button to every listing, review reports promptly, and tell sellers why you removed their listing.
- Write a breach plan that meets the GDPR's 72-hour deadline, and a short risk assessment if you have UK users.
- Keep software patched and backups out of reach of the web server; revoke access the day someone leaves.
- If you host business sellers, check whether the DSA trader rules or the INFORM Consumers Act apply to you.
Doing this with Yclas
If you run your marketplace on Yclas, several items on the checklist are built in. Site owners can turn on two-step login with an authenticator app or SMS, and give team members moderator or translator roles instead of sharing the admin account. An audit log records admin actions, and nobody can edit or delete it. The cookie banner offers separate choices, users can download their data, and account deletion is confirmed by email.
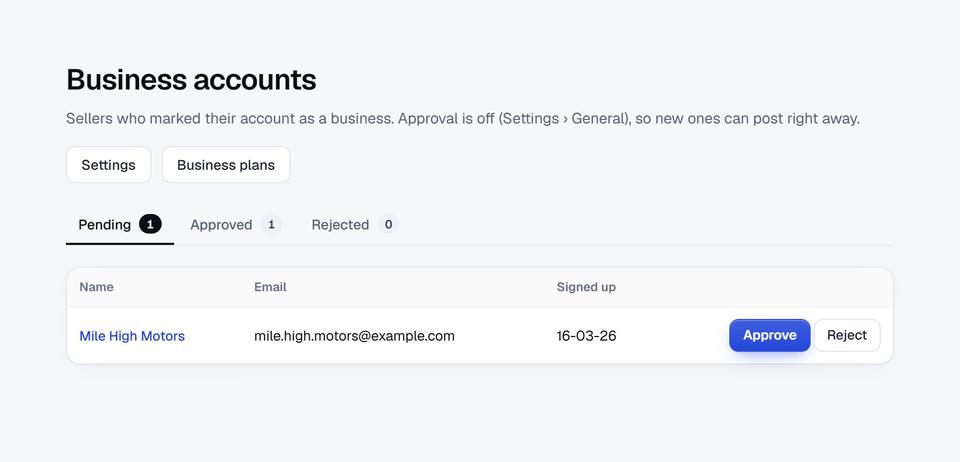
For the DSA, every listing has a Report button with DSA reasons, reports go to a reports queue, and when the owner acts the seller gets a statement of reasons by email. Business accounts can be approved with their trader details. Seller verification lets sellers upload an ID or business document; your team approves or rejects it, and the document is deleted once decided. Owners choose how listings are published: straight away, after approval, after the seller confirms their email, or after payment. On the Starter, Professional and Marketplace plans (see pricing), an AI check screens every new listing for scam patterns and your own rules, and holds risky ones in a moderation queue with the reason. Buyer-seller messages warn users when someone asks for gift cards, wire transfers or one-time codes, and listing pages show safety tips. Spam protection includes captcha, disposable email blocking, banned words, Akismet, blocked emails and domains, and limits on listings, messages and login attempts. See the full list on our trust and safety page, or try it with the free 15-day trial.
The rest of the trust and safety guide covers reviews, ratings and verified sellers, disputes and customer support.
Frequently asked questions
Does the GDPR apply to a small marketplace outside the EU?
Yes, if it offers its services to people in the EU or tracks their behaviour, for example with analytics or ads. The GDPR has no size or revenue threshold, although some record-keeping duties are lighter for small organisations.
Does the CCPA apply to my classifieds site?
Only if you meet one of its tests: over $26,625,000 in annual revenue, buying, selling or sharing data on 100,000 or more California consumers or households, or earning half your revenue from selling or sharing data. Other US states have their own thresholds.
What does the Digital Services Act require from a small marketplace?
Every platform with EU users needs a way to report illegal content, must act on reports, must tell users why their content was removed, and must publish clear terms and a contact point. The trader traceability rules and most extra platform duties do not apply to micro and small enterprises.
Is SMS two-factor authentication still safe?
It is much better than a password alone, but it can be defeated by SIM swapping, and NIST now classes it as "restricted". Use an authenticator app or passkeys where possible, especially for admin accounts, and keep SMS as a fallback.
Do I need to be PCI compliant if I use a payment provider?
Yes, but it is much simpler. If the provider takes all card entry on its own page or embedded form, you can usually validate with the short SAQ A questionnaire. Ask your provider what evidence you need.
How quickly must I report a data breach?
Under the GDPR, to your data protection authority within 72 hours of becoming aware of it, unless it is unlikely to put anyone at risk. US state laws set their own deadlines for notifying residents.